Course Objectives
Q1. What will I learn from ISC2 ISSMP Training?
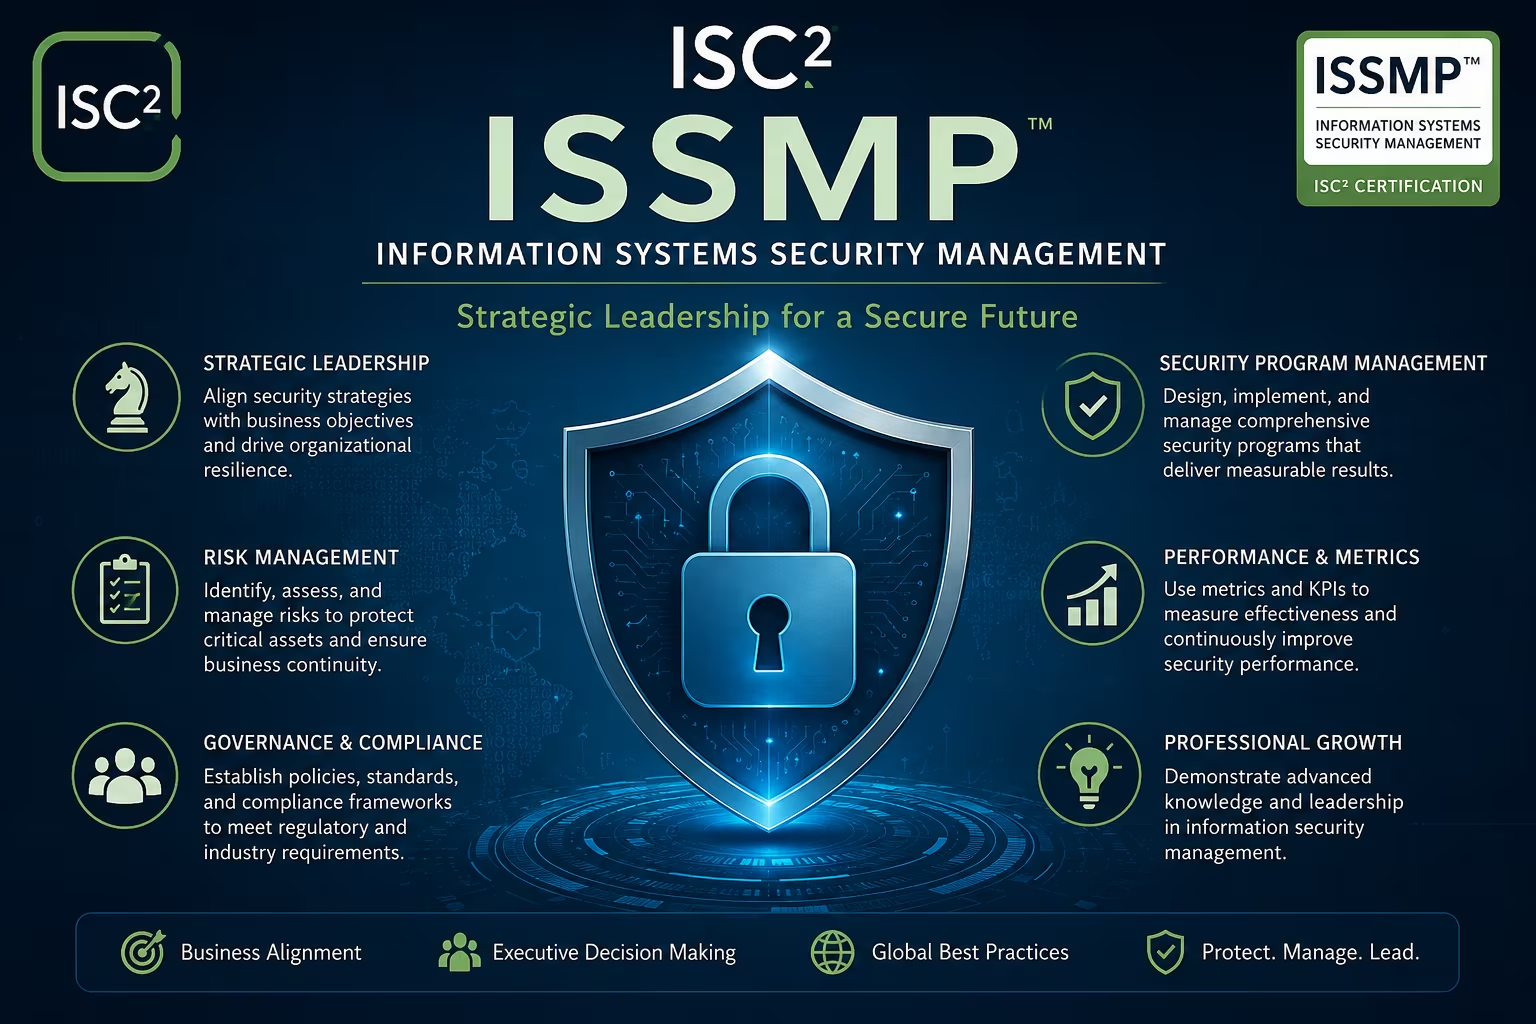
You will learn how to manage enterprise information security programs, establish security governance, assess organizational risks, and develop strategic security initiatives. The training also helps you understand the responsibilities of senior information security management professionals.
Q2. How does ISC2 ISSMP improve my security management skills?
The course develops advanced skills in security governance, enterprise risk management, security program development, incident management, resource planning, and strategic security leadership. Practical scenarios help you understand how security decisions are made at an organizational level.
Q3. Is ISC2 ISSMP suitable for experienced cybersecurity professionals?
Yes. ISC2 ISSMP is particularly relevant for professionals progressing toward information security management and leadership responsibilities. The training focuses on strategic and managerial aspects of cybersecurity rather than only technical security operations.
Q4. What practical knowledge will I gain from this course?
You will practice security program planning, enterprise risk assessment, governance development, security performance measurement, incident management planning, resource management, and executive security reporting through realistic enterprise scenarios.
Q5. How can ISC2 ISSMP support my cybersecurity career?
ISC2 ISSMP can strengthen your ability to manage enterprise security programs and communicate security requirements to business and executive stakeholders. It is useful for professionals targeting senior information security, security management, governance, risk, and cybersecurity leadership responsibilities.
Popular Techniques Covered in This Course
Security Leadership
Information Security Governance
Enterprise Security Strategy
Risk Management
Security Program Management
Security Architecture Management
Security Policy Development
Security Resource Planning
Incident Management
Business Continuity Planning
Compliance Management
Security Performance Management
Executive Security Reporting
Security Awareness Management
Strategic Cybersecurity Management
Get Hands-on Knowledge about Real-Time Projects
Project 1
Enterprise Information Security Strategy Project
Develop an enterprise-level information security strategy aligned with business objectives, organizational risks, security priorities, governance requirements, and long-term cybersecurity goals.
Project 2
Security Governance & Risk Management Project
Create a practical security governance framework covering policies, roles and responsibilities, risk identification, risk assessment, risk treatment, security controls, reporting, and management oversight.
Project 3
Enterprise Security Program Development Project
Design a complete security program including security objectives, implementation roadmap, control requirements, resource planning, security metrics, performance indicators, and continuous improvement activities.
Project 4
Cybersecurity Incident & Business Resilience Project
Develop an enterprise incident management and business resilience strategy covering incident response, crisis management, business continuity, disaster recovery, communication, recovery planning, and post-incident improvement.
Project 5
Executive Security Management Dashboard Project
Build a management-level security reporting framework containing security KPIs, risk indicators, compliance status, security performance metrics, resource requirements, and executive-level recommendations.
Key Features
Edubrights offers ISC2 ISSMP – Information Systems Security Management Training in virtual mode with expert trainers. Here are the key features,
40 Hours Course Duration
100% Job Oriented Training
Industry Expert Faculties
Free Demo Class Available
Completed 500+ Batches
Certification Guidance
Curriculum
Module 1: Information Security Leadership & Management
- Information Security Management Fundamentals
- Role of the Information Security Manager
- Security Leadership Principles
- Security Management Responsibilities
- Business and Security Alignment
- Security Leadership Communication
- Stakeholder Management
- Security Decision-Making
- Ethical Security Leadership
Module 2: Information Security Governance
- Security Governance Fundamentals
- Corporate Governance
- Security Policies and Standards
- Security Procedures and Guidelines
- Governance Frameworks
- Security Roles and Responsibilities
- Accountability and Oversight
- Security Committees
- Governance Metrics and Reporting
Module 3: Enterprise Security Strategy
- Security Strategy Development
- Business Objectives and Security
- Enterprise Security Planning
- Strategic Security Roadmaps
- Security Program Prioritization
- Security Performance Metrics
- Executive Security Reporting
- Strategic Decision-Making
- Business-Security Alignment
Module 4: Enterprise Risk Management
- Information Security Risk Fundamentals
- Risk Identification
- Risk Analysis
- Risk Evaluation
- Risk Treatment
- Risk Acceptance
- Risk Transfer
- Risk Avoidance
- Enterprise Risk Registers
- Risk Communication
Module 5: Security Program Development
- Security Program Planning
- Security Program Objectives
- Security Program Lifecycle
- Security Control Selection
- Security Program Implementation
- Security Program Documentation
- Security Metrics
- Program Performance Monitoring
- Continuous Program Improvement
Module 6: Security Architecture & Technology Management
- Enterprise Security Architecture
- Security Architecture Principles
- Network Security Architecture
- Application Security
- Cloud Security Management
- Identity and Access Management
- Data Security
- Security Technology Management
- Technology Risk Management
Module 7: Security Resource Management
- Security Team Structure
- Workforce Planning
- Security Skills Management
- Resource Allocation
- Security Budget Planning
- Vendor Management
- Security Service Providers
- Security Awareness Programs
- Team Performance Management
Module 8: Incident Management & Business Resilience
- Security Incident Management
- Incident Response Planning
- Incident Detection and Analysis
- Incident Containment
- Incident Eradication
- Incident Recovery
- Crisis Management
- Business Continuity Planning
- Disaster Recovery
- Incident Lessons Learned
Module 9: Security Risk & Compliance Management
- Regulatory Compliance
- Security Standards
- Compliance Management
- Internal Security Requirements
- External Regulatory Requirements
- Security Assessments
- Audit Management
- Compliance Reporting
- Risk-Based Compliance
- Corrective Action Planning
Module 10: Security Operations & Performance Management
- Security Operations Management
- Security Monitoring
- Security Metrics
- Key Performance Indicators
- Key Risk Indicators
- Security Reporting
- Operational Risk Management
- Security Control Monitoring
- Performance Improvement
- Management Dashboards
Module 11: Security Culture, Awareness & Communication
- Security Culture Development
- Security Awareness Programs
- Security Training Programs
- Executive Communication
- Security Policy Communication
- Stakeholder Engagement
- Security Leadership Communication
- Security Ethics
- Human Risk Management
- Security Program Adoption
Module 12: ISC2 ISSMP Enterprise Security Management Project
- Enterprise Security Assessment
- Security Governance Review
- Enterprise Risk Assessment
- Security Strategy Development
- Security Program Planning
- Security Architecture Review
- Incident Management Planning
- Security Metrics Development
- Executive Security Reporting
- Final Security Management Project
Receive Training From Our Skilled and Effective Trainers
Experience in the Industry
Learn from experienced ISC2 ISSMP professionals who have worked on enterprise information security management, cybersecurity leadership, governance, risk management, security program development, and strategic security initiatives across technology, banking, healthcare, consulting, and enterprise environments.
Backgrounds at the Top
Our ISC2 ISSMP trainers bring hands-on experience managing security programs, developing enterprise security strategies, implementing governance frameworks, assessing organizational risks, coordinating security teams, and aligning cybersecurity initiatives with business objectives.
Clear & Effective Teaching
Complex information security management concepts are explained using enterprise security scenarios, governance case studies, risk management exercises, incident management examples, security strategy workshops, and executive reporting situations, helping learners understand how senior security professionals make strategic decisions.
Hands-On Learning Focus
Students gain practical experience through enterprise risk assessments, security governance exercises, security program development, incident management planning, security metrics creation, resource management activities, compliance assessments, and real-world information security management projects designed to build leadership-oriented skills.
Up-to-Date Knowledge
Our instructors continuously update the ISC2 ISSMP curriculum to align with current ISC2 certification domains, cybersecurity governance practices, enterprise risk management approaches, security leadership principles, compliance requirements, security management frameworks, and evolving enterprise cybersecurity trends.
About Our Course Certification*
ISC2 ISSMP – Information Systems Security Management Professional training at Edubrights is designed for experienced cybersecurity and information security professionals who want to strengthen their expertise in security leadership, governance, enterprise risk management, and strategic security program management. The course covers information security governance, enterprise security strategy, risk assessment, security program development, security architecture management, incident management, resource planning, compliance, security performance, and executive communication. Learners gain practical exposure through enterprise case studies, guided exercises, security management scenarios, and real-world projects. The training also supports preparation for the ISC2 ISSMP certification by helping learners understand the key security management concepts and professional practices required for advanced information security responsibilities.
Course FAQs
1. What is ISC2 ISSMP certification?
ISC2 ISSMP stands for Information Systems Security Management Professional. It is an advanced cybersecurity management certification focused on security leadership, governance, risk management, security program development, and enterprise security management. The certification is designed for experienced professionals who manage or lead information security functions within organizations.
2. Who is eligible for ISC2 ISSMP training?
ISC2 ISSMP training is most suitable for experienced cybersecurity and information security professionals, security managers, IT managers, security architects, and professionals moving toward security leadership roles. Candidates should ideally have practical experience in information security management and a strong understanding of cybersecurity concepts before beginning advanced ISSMP preparation.
3. Do I need cybersecurity experience before learning ISSMP?
Yes, prior cybersecurity or information security experience is recommended because ISSMP focuses heavily on management, governance, risk, leadership, and strategic security decisions. Beginners can study the concepts, but professionals with practical security experience will generally find it easier to understand and apply the advanced management topics.
4. What are the prerequisites for ISC2 ISSMP training?
A strong foundation in information security, cybersecurity governance, risk management, security controls, and enterprise security concepts is recommended. Familiarity with security policies, compliance requirements, incident management, and organizational security practices can also help learners understand the course more effectively.
5. How long does ISC2 ISSMP training take?
The duration depends on the training format, learner experience, and depth of practical exercises. A structured course can cover the ISSMP domains through instructor-led sessions, case studies, revision activities, and practice exercises. Learners should also allocate additional preparation time for reviewing concepts and preparing for the certification examination.
6. What will I learn in an ISC2 ISSMP course?
You will learn advanced information security management concepts including security leadership, governance, enterprise risk management, security program development, security architecture management, incident management, resource planning, compliance, security performance measurement, and strategic security planning.
7. Is ISC2 ISSMP suitable for working professionals?
Yes. The course is particularly relevant for working professionals who already have cybersecurity or information security experience and want to develop stronger management and leadership capabilities. Practical case studies and enterprise security scenarios can help professionals connect the concepts with responsibilities they may encounter in real organizational environments.
8. Does the course include practical training?
Yes. Practical learning can include enterprise risk assessment exercises, security governance scenarios, security program planning, incident management activities, security metrics development, compliance assessments, and executive security reporting. These exercises help learners understand how information security management concepts can be applied beyond theoretical study.
9. Does ISC2 ISSMP training prepare me for certification?
The training can support certification preparation by covering the major ISSMP knowledge areas through structured lessons, domain-focused revision, practical scenarios, and practice questions. Learners should also review the current official ISC2 certification requirements and examination information before scheduling their examination.
10. What skills are important for an ISSMP professional?
Important skills include security leadership, governance, enterprise risk management, security program management, strategic planning, compliance management, incident management, security architecture oversight, stakeholder communication, and security performance measurement. Strong business understanding and decision-making abilities are also valuable for senior security management responsibilities.
11. Can cybersecurity managers benefit from ISC2 ISSMP?
Yes. Cybersecurity managers can use ISSMP preparation to strengthen their understanding of enterprise security leadership, governance, risk management, resource planning, security program development, and strategic decision-making. The course is particularly relevant to professionals responsible for coordinating security initiatives with organizational goals and business requirements.
12. What practical projects can I work on during ISSMP training?
Projects may include developing an enterprise security strategy, creating a security governance framework, conducting an organizational risk assessment, designing a security program roadmap, developing security metrics, and preparing an incident management strategy. These projects help learners practice the responsibilities associated with information security management.
13. Is ISC2 ISSMP in demand in the cybersecurity industry?
Organizations increasingly require professionals who can manage cybersecurity programs while aligning security initiatives with business, compliance, and risk requirements. ISSMP focuses on these management-level capabilities, making the knowledge relevant to enterprise security governance, risk management, security program leadership, and information security management functions.
14. Can ISSMP help me move into a cybersecurity leadership role?
ISSMP can strengthen the management and strategic knowledge required for senior cybersecurity responsibilities. It covers areas such as leadership, governance, risk, security programs, resource management, and communication, helping experienced professionals demonstrate broader security management knowledge alongside their existing technical and professional experience.
15. Why choose Edubrights for ISC2 ISSMP Training in Chennai?
Edubrights focuses on practical, industry-oriented learning through instructor-led sessions, enterprise security scenarios, guided exercises, certification preparation, and career-focused activities. The training is designed to help experienced cybersecurity professionals understand how ISSMP concepts apply to real information security management responsibilities.
Get Training Quote for Free
Testimonials
Hear What Our Students Say
"Transform your life through Education, hear it from our Alumni"

6 LPA
Fathima
Student
Software Engineer
"Transform your life through Education, hear it from our Alumni"
8 LPA
Siddharth
NIELSON IQ
Data Analyst
"Transform your life through Education, hear it from our Alumni"
8 LPA
Rahul
Student
Data Scientist