Course Objectives
1. What will you learn in the IBM QRadar – SIEM & Security Analytics course?
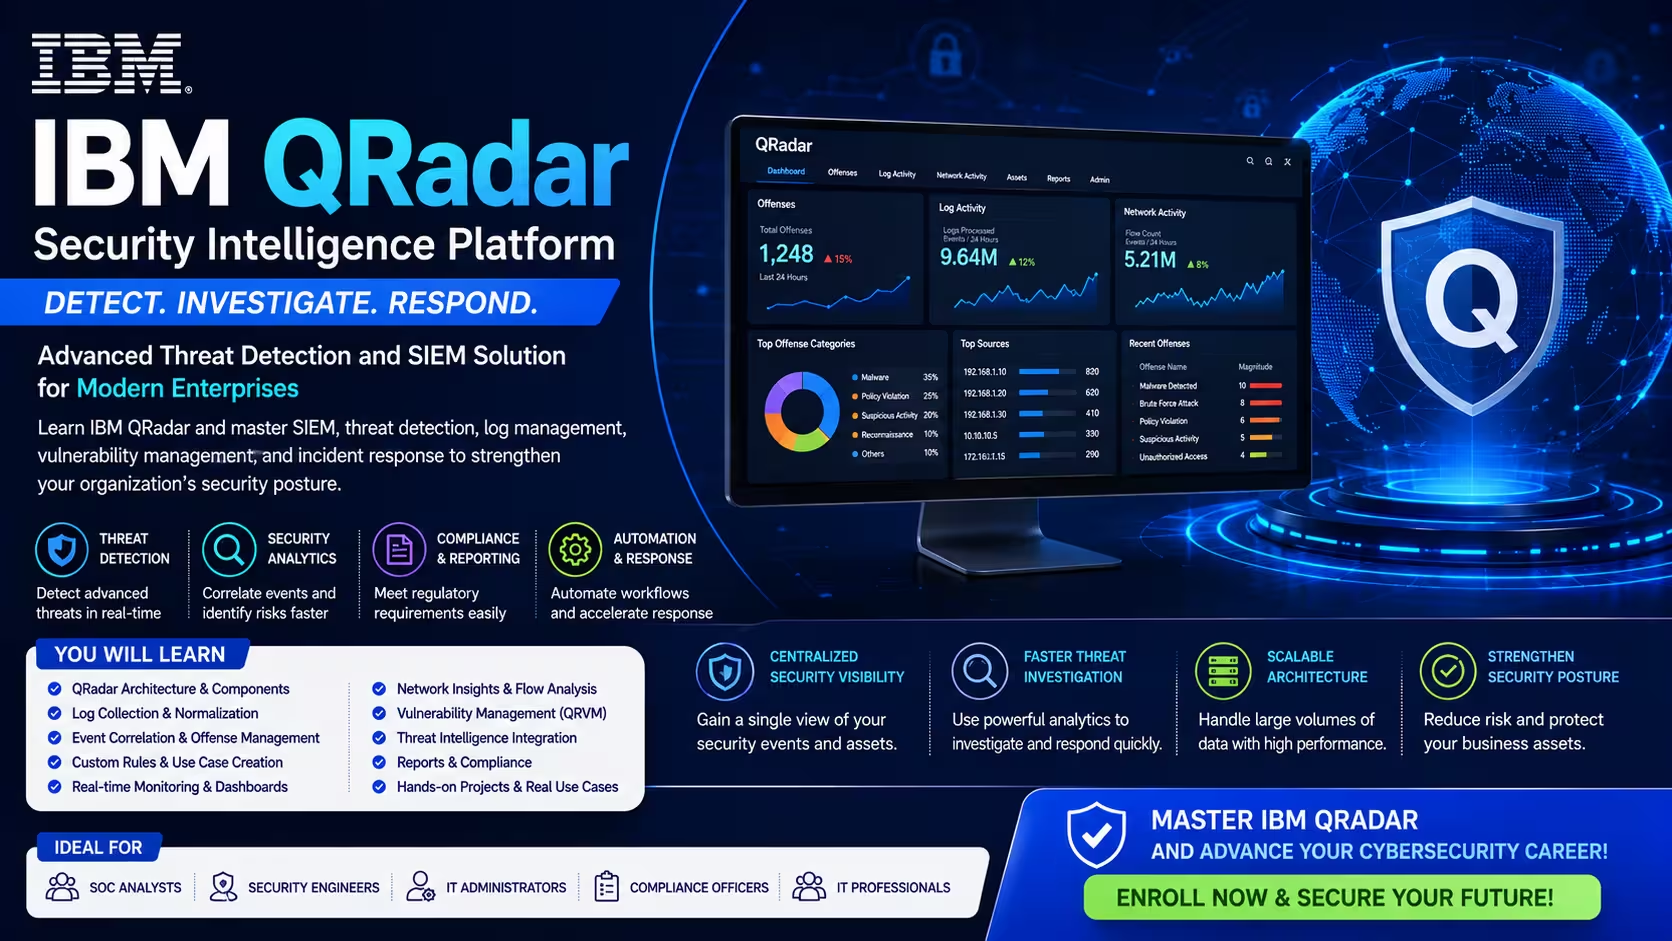
You will learn how to deploy, configure, administer, and monitor enterprise security environments using IBM QRadar SIEM. The course covers Security Information and Event Management (SIEM), log management, event correlation, network flow analysis, threat detection, offense investigation, incident response, vulnerability integration, security analytics, and compliance monitoring.
2. How does this course prepare you for real-world IBM QRadar projects?
The course provides hands-on experience in collecting security logs, monitoring network traffic, creating correlation rules, investigating security incidents, responding to cyber threats, integrating security devices, and protecting enterprise environments using IBM QRadar.
3. What practical skills will you develop during the training?
You will gain expertise in IBM QRadar architecture, log source integration, event collection, flow monitoring, custom rules, offenses, dashboards, reports, asset profiling, user behavior analytics, security monitoring, threat intelligence integration, and incident investigation.
4. How will real-time projects improve your IBM QRadar skills?
You will work on practical projects involving Security Operations Center (SOC) monitoring, cyberattack detection, insider threat monitoring, compliance reporting, malware investigations, phishing detection, and enterprise security analytics.
5. What career opportunities can you pursue after learning IBM QRadar – SIEM & Security Analytics?
This course prepares you for roles such as IBM QRadar Administrator, SIEM Engineer, SOC Analyst, Cybersecurity Analyst, Security Operations Engineer, Incident Response Analyst, Threat Detection Engineer, Security Consultant, and Security Analyst.
Popular Techniques Covered in This Course
Security Information and Event Management (SIEM) Fundamentals
IBM QRadar Architecture and Components
Log Source Configuration and Event Collection
Network Flow Analysis and Monitoring
Correlation Rules and Offense Management
Threat Detection and Incident Investigation
Security Dashboards, Reports, and Compliance Monitoring
Threat Intelligence and Vulnerability Integration
QRadar Administration, Performance Tuning, and Troubleshooting
Security Operations Center (SOC) Best Practices
Get Hands-on Knowledge about Real-Time Projects
Project 1
Project 1: Enterprise SOC Monitoring
Deploy IBM QRadar to collect logs from firewalls, servers, endpoints, and applications while monitoring security events in real time.
Project 2
Project 2: Cyber Threat Detection System
Build a security monitoring solution that detects malware, phishing attempts, brute-force attacks, privilege escalation, and unauthorized access.
Project 3
Project 3: Security Incident Investigation
Configure custom correlation rules to investigate suspicious activities, generate offenses, and automate security incident response workflows.
Project 4
Project 4: Compliance and Audit Reporting
Develop dashboards and reports for compliance standards such as ISO 27001, PCI DSS, HIPAA, and GDPR using IBM QRadar.
Project 5
Project 5: Threat Intelligence Integration
Integrate IBM QRadar with external threat intelligence feeds to improve threat detection, event correlation, and proactive security monitoring.
Key Features
Edubrights offers IBM QRADAR – SIEM & SECURITY ANALYTICS Training in virtual mode with expert trainers. Here are the key features,
40 Hours Course Duration
100% Job Oriented Training
Industry Expert Faculties
Free Demo Class Available
Completed 500+ batches
Certification Guidance
Curriculum
Module 1: SIEM Concepts and IBM QRadar Architecture
- Security Information and Event Management (SIEM) fundamentals
- QRadar architecture: Console, Event Processor, Flow Processor, and Data Nodes
- QRadar deployment models: on-premise, cloud, and SaaS
- Navigating the QRadar SIEM console: dashboards, offenses, and log activity
Module 2: Log Sources and Data Collection
- Log source types: syslog, JDBC, SNMP, and API-based collection
- Configuring log sources: firewall, Windows, Linux, and cloud platforms
- QRadar DSMs (Device Support Modules): parsing and normalisation
- Universal DSM and custom log source parser creation
Module 3: Rules and Offense Management
- QRadar rule engine: building blocks, tests, and actions
- Creating custom detection rules: threshold, behavioural, and anomaly
- Offense generation: correlating events into actionable alerts
- Offense triage: investigation workflow and false positive tuning
Module 4: Network Flow Analysis
- QFlow Collector and VFlow for network traffic analysis
- Flow data analysis: top talkers, protocols, and geographic mapping
- Detecting lateral movement and exfiltration using flow data
- Combining event and flow data for enriched threat detection
Module 5: QRadar Use Cases and Threat Detection
- Detecting brute force, privilege escalation, and account compromise
- Ransomware and malware activity detection rules
- Insider threat detection: DLP and data exfiltration indicators
- MITRE ATT&CK framework mapping in QRadar rules
Module 6: Reference Sets, Watchlists, and Threat Intelligence
- Reference sets: IP, URL, and hash-based allow/block lists
- Threat intelligence integration: IBM X-Force and STIX/TAXII feeds
- App Framework: QRadar apps from the IBM Security App Exchange
- User Behaviour Analytics (UBA) app for insider threat detection
Module 7: Reporting and Compliance
- QRadar report templates: executive summary and compliance reports
- Custom report builder: queries, filters, and scheduled delivery
- Compliance content: PCI-DSS, SOX, and HIPAA report packs
- QRadar API for custom integrations and data extraction
Module 8: Capstone Project and Assessment
- QRadar log source configuration and parsing exercise
- Custom detection rule creation and offense investigation simulation
- Compliance reporting and executive dashboard build
- Final assessment and course certification
Receive Training From Our Skilled and Effective Trainers
Experience in the Industry Gain expertise from IBM QRadar-certified SIEM engineers who have deployed and operated QRadar environments for enterprise SOCs, financial institutions, and managed security service providers processing millions of events per day.
Backgrounds at the Top Our QRadar trainers have built detection engineering programmes, tuned SIEM rules, and investigated security incidents using QRadar at global banks, telecommunications companies, and government security operations centres.
Clear & Effective Teaching QRadar log source configuration, DSM parsing, rule engine, offense management, flow analysis, threat intelligence integration, and reporting are explained clearly with real SOC analyst workflows and detection scenarios.
Hands-On Learning Focus Students configure log sources, build custom detection rules, investigate simulated offenses, analyse network flows, and create compliance reports through structured hands-on lab exercises.
Up-to-Date Knowledge Trainers keep content current with the latest QRadar releases, QRadar SIEM on Cloud updates, IBM Security QRadar Suite enhancements, and evolving SOC detection engineering methodologies.
Professional IBM QRadar – SIEM & Security Analytics Certification
The Professional IBM QRadar – SIEM & Security Analytics Certification validates your expertise in implementing and managing enterprise Security Information and Event Management (SIEM) solutions using IBM QRadar.
Course FAQs
1. What is IBM QRadar?
Answer: IBM QRadar is a leading Security Information and Event Management (SIEM) platform that collects, analyzes, and correlates security events to detect cyber threats and security incidents.
2. What is SIEM?
Answer: SIEM (Security Information and Event Management) combines log management, security event monitoring, threat detection, and incident response into a centralized security platform.
3. What are Offenses in IBM QRadar?
Answer: Offenses are prioritized security alerts generated when QRadar detects suspicious activities or correlated security events requiring investigation.
4. What is Network Flow Analysis?
Answer: Network Flow Analysis monitors network communication patterns to identify suspicious traffic, abnormal behavior, and potential cyber threats.
5. Can IBM QRadar integrate with other security tools?
Answer: Yes. IBM QRadar integrates with firewalls, IDS/IPS, antivirus solutions, endpoint security platforms, cloud services, vulnerability scanners, and threat intelligence feeds.
6. Which industries use IBM QRadar?
Answer: Banking, healthcare, insurance, government, retail, telecommunications, manufacturing, energy, finance, and enterprise IT organizations use IBM QRadar.
7. Is IBM QRadar suitable for Security Operations Centers (SOC)?
Answer: Yes. IBM QRadar is widely used by SOC teams for real-time threat monitoring, incident detection, forensic investigations, and compliance reporting.
8. Does the course include practical projects?
Answer: Yes. The course includes hands-on projects involving SOC monitoring, log analysis, threat detection, compliance reporting, and security incident investigations.
9. Is IBM QRadar beginner-friendly?
Answer: Yes. Basic knowledge of networking, cybersecurity, and operating systems is recommended. The course begins with SIEM fundamentals before advancing to IBM QRadar administration.
10. Why should professionals learn IBM QRadar?
Answer: IBM QRadar is one of the industry's leading SIEM platforms, making QRadar skills highly valuable for cybersecurity, SOC operations, and threat detection careers.
Get Training Quote for Free
Testimonials
Hear What Our Students Say
"Transform your life through Education, hear it from our Alumni"
8 LPA
Rahul
Student
Data Scientist
"Transform your life through Education, hear it from our Alumni"
8 LPA
Siddharth
NIELSON IQ
Data Analyst
"Transform your life through Education, hear it from our Alumni"

6 LPA
Fathima
Student
Software Engineer