Course Objectives
1. What exactly Ethical Hacking training cover?
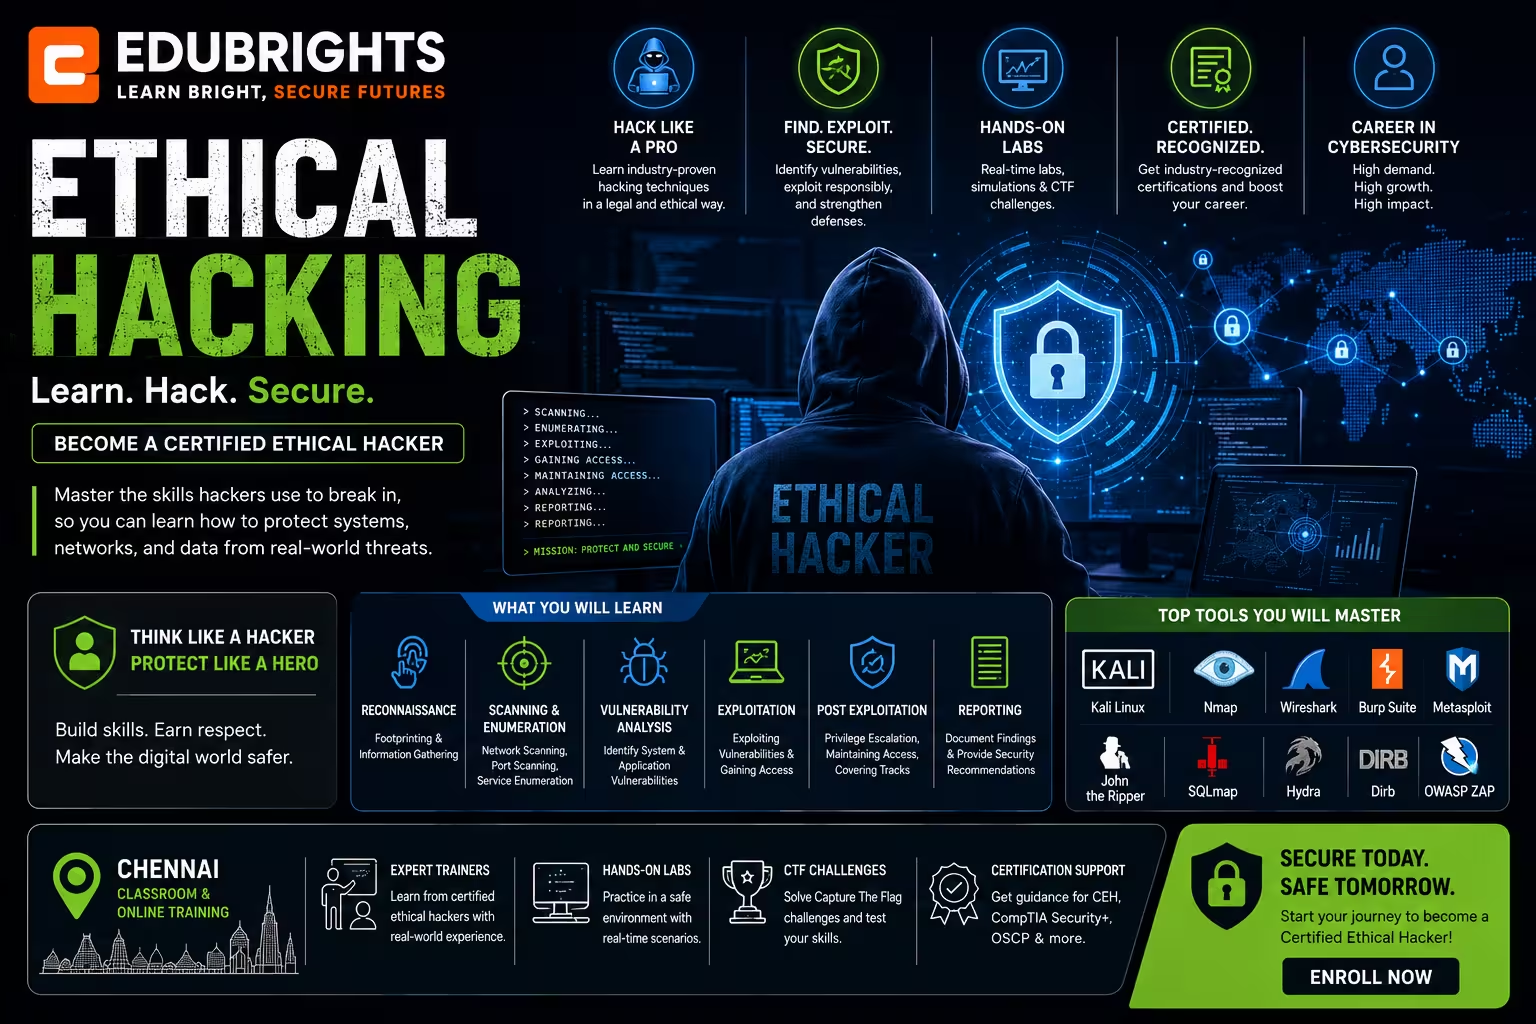
Ethical Hacking training covers network security, vulnerability assessment, penetration testing, and malware analysis. It teaches tools and techniques for footprinting, scanning, system hacking, and social engineering. The course emphasizes legal and ethical hacking practices, cryptography, and defense strategies. Hands-on labs with real-world scenarios prepare learners for cybersecurity roles.
2. Why is Ethical Hacking important?
You will understand how companies use ethical hackers to protect their digital assets from real cyber threats.
3. How do you perform penetration testing?
You will master tools and methods to test network, web application, and system security.
4. Which skills are needed for Ethical Hacking?
You will develop practical skills in reconnaissance, exploitation, and reporting.
5. How do you start a career in Ethical Hacking?
You will build a strong foundation to work as a penetration tester or security analyst.
Popular Techniques Covered in This Course
1.Network Security
2.Risk Management and Assessment
3.Incident Response and Security Operations
4.Ethical Hacking and Penetration Testing
5.Programming and Scripting
6.Cloud Security
7.Operating Systems and System Administration
8.Security Tools and Technologies
9.Communication and Documentation
10.Emerging Technologies
Get Hands-on Knowledge about Real-Time Projects
Project 1
Project 1: Network Penetration Testing
Perform a full ethical hack on a simulated corporate network.
Project 2
Project 2: Web Application Security Testing
Identify and exploit vulnerabilities in a web application.
Project 3
Project 3: Wireless Network Assessment
Test and secure a wireless network environment.
Project 4
Project 4: Social Engineering Simulation
Execute and analyze a controlled social engineering attack.
Project 5
Project 5: Complete Security Assessment
Conduct end-to-end ethical hacking on a target organization.
Key Features
Edubrights offers Ethical Hacking Training in virtual mode with expert trainers. Here are the key features,
40 Hours Course Duration
100% Job Oriented Training
Industry Expert Faculties
Free Demo Class Available
Completed 500+ Batches
Certification Guidance
Curriculum
Module 1: Introduction to Ethical Hacking
- What is Ethical Hacking?
- Hackers fall into three divisions: White Hat, Black Hat, and Gray Hat.
- Cybersecurity Ideas and the Five Ethical Hacking Approaches
- Legal and Ethical Issues, Cyber Laws and Compliance
Module 2: Footprinting and Reconnaissance
- Information Gathering Techniques (Passive and Active)
- DNS Enumeration, WHOIS Lookup, Social Engineering
- Tools: Maltego, Recon-ng, Google Hacking
Module 3: Scanning and Enumeration
- Network Scanning Techniques
- Vulnerability Scanning and Assessment
- Enumeration of Network Resources and Services
- Tools: Nmap, Nessus, OpenVAS
Module 4: System Hacking
- Exploiting System Vulnerabilities
- Privilege Escalation Techniques
- Password Cracking and Bypassing Security Controls
- Use of Metasploit Framework
Module 5: Malware Analysis and Threats
- Types of Malware: Viruses, Worms, Trojans, Ransomware
- Malware Propagation and Detection
- Anti-Malware Strategies and Incident Response
Module 6: Sniffing and Packet Analysis
- Network Packet Capture and Analysis
- Man-in-the-Middle (MITM) Attacks
- Tools: Wireshark, Tcpdump
Module 7: Social Engineering
- Phishing, Pretexting, Baiting Techniques
- Psychological Manipulation and Defense Mechanisms
- User Awareness and Training
Module 8: Denial-of-Service (DoS) and Distributed DoS (DDoS) Attacks
- Attack Vectors and Tools
- Detection and Mitigation Strategies
Module 9: Web Application Security
- Common Vulnerabilities: SQL Injection, Cross-Site Scripting (XSS), CSRF
- Secure Coding Practices
- Web Application Firewalls and Security Testing Tools (Burp Suite)
Module 10: Wireless Network Security
- Wireless Encryption Protocols (WEP, WPA, WPA2)
- Wireless Attacks: Deauthentication, Fake Access Points
- WiFi Hacking Tools and Defense
Module 11: Cryptography
- Symmetric and Asymmetric Encryption Algorithms
- Hashing, Digital Signatures, Certificates
- Steganography
Module 12: Penetration Testing Methodologies
- Planning and Scoping
- Exploitation and Post-Exploitation
- Reporting and Documentation
Module 13: Incident Response and Handling
- Detecting and Responding to Security Incidents
- Forensics Basics
- Risk Management and Compliance
Module 14: Hacking's Ethical and Legal Concerns
- Cyber Laws and Regulations
- Ethical Guidelines for Security Professionals
Module 15: Emerging Threats and Technologies
- Cloud Security Challenges
- IoT Security
- AI and Machine Learning in Cybersecurity
Module 16: Hands-on Labs and Real-World Scenarios
- Practical Exercises with Kali Linux
- Capture The Flag (CTF) Challenges
- Use of Tools like Metasploit, Nmap, Wireshark, Burp Suite
Receive Training From Our Skilled and Effective Trainers
Experience in the Industry Gain knowledge from experts with practical Ethical Hacking project experience in a variety of sectors.
Backgrounds at the Top Prominent corporations such as hcl, tcs , accenture and cognizant employ trainers.
Clear & Effective Teaching Excellent communication and real-world examples simplify complex subjects.
Hands-On Learning Focus Students can apply their abilities in real-world situations with the use of case studies and real-time projects.
Up-to-Date Knowledge Trainers stay current with the latest tools, techniques and best practices.
Succeed Our Resourceful Certification
A Ethical Hacking certification validates your expertise in protecting computer systems, networks, and data from cyber threats through practical skills and industry best practices. It enhances your career prospects by demonstrating proficiency in areas like ethical hacking, risk management, and incident response.
Course FAQs
Q1: What makes the ethical hacking course in Chennai at Edubrights stand out?
A: Our ethical hacking course in Chennai stands out due to its comprehensive, industry-aligned curriculum that covers both offensive penetration testing and defensive security operations. We emphasize hands-on learning with dedicated virtual lab access, real-world corporate simulation projects, and practical exposure to industry-standard tools like Kali Linux, Metasploit, and Burp Suite. Additionally, our dedicated placement support, experienced corporate trainers, and focus on building a strong professional portfolio ensure that our students are thoroughly prepared for the highly competitive Chennai IT and cybersecurity job markets.
Q2: Can freshers or non-IT students join this ethical hacking training in Chennai?
A: Absolutely, fresh graduates, non-IT professionals, and career switchers are highly encouraged to join. We start the curriculum with foundational networking, operating system, and basic programming concepts before gradually introducing complex hacking methodologies. This structured approach ensures that even those with limited technical backgrounds can comfortably grasp cybersecurity principles, build practical skills, and successfully transition into high-demand ethical hacking roles.
Q3: Does the course prepare students for the Certified Ethical Hacker (CEH) exam?
A: Yes, our curriculum is explicitly aligned with the objectives of major industry certifications, particularly the EC-Council Certified Ethical Hacker (CEH) exam. We provide dedicated exam preparation modules, practice tests, and strategic guidance to help you confidently navigate and pass this globally recognized certification, which significantly boosts your credibility and employability in the cybersecurity domain.
Q4: What kind of hands-on virtual lab environments are provided to students?
A: Theoretical knowledge is insufficient for mastering ethical hacking, which is why we provide every student with dedicated access to real-time, cloud-based virtual lab environments. This hands-on access allows you to practice setting up vulnerable machines, executing penetration tests, and configuring security tools in a safe, sandboxed environment without risking your personal hardware or violating any legal boundaries, ensuring you build practical muscle memory.
Q5: Are there specific modules on web application penetration testing and the OWASP Top 10?
A: Yes, web application security is a critical focus area, and we provide deep, hands-on training on the OWASP Top 10 vulnerabilities. You will learn how to identify, exploit, and remediate common web flaws such as SQL Injection, Cross-Site Scripting, Broken Access Control, and Insecure Deserialization using tools like Burp Suite and OWASP ZAP, making you highly effective in web VAPT roles demanded by Chennai’s tech companies.
Q6: How does the training address network security and infrastructure hacking?
A: Network security is a foundational pillar of our curriculum, and we cover it extensively through practical exercises. You will learn how to perform advanced network scanning with Nmap, analyze traffic with Wireshark, exploit network vulnerabilities using Metasploit, and understand how to bypass or configure firewalls and intrusion detection systems, giving you a complete understanding of network defense and offense.
Q7: What real-world projects are included in the ethical hacking curriculum?
A: You will work on multiple end-to-end real-time projects that simulate actual corporate security scenarios relevant to Chennai’s industries. These include conducting a full Vulnerability Assessment and Penetration Testing engagement on a mock corporate network, setting up a SIEM dashboard for real-time threat monitoring, and executing an incident response playbook for a simulated ransomware attack, all of which will form a strong, verifiable portfolio for your resume.
Q8: What kind of placement support is provided for ethical hacking students in Chennai?
A: We provide comprehensive, job-oriented placement assistance tailored specifically for the Chennai market. This includes personalized resume building that highlights your security skills and project experience, LinkedIn profile optimization for tech recruiters, rigorous mock technical and HR interviews, and direct referrals to our extensive network of hiring partners, including top IT consulting firms, cybersecurity startups, and multinational corporations based in the city.
Q9: Who are the trainers delivering the ethical hacking course in Chennai?
A: Our trainers are senior cybersecurity professionals and certified ethical hackers with over a decade of hands-on experience working on live security audits, penetration testing, and SOC management projects in top multinational corporations. They bring real-world attack scenarios, industry best practices, and practical troubleshooting techniques directly into the classroom, ensuring you learn exactly what is expected in a professional corporate environment.
Q10: Are there weekend or fast-track batches available for working professionals in Chennai?
A: Yes, we understand the demanding schedules of working professionals in Chennai’s IT and corporate sectors, which is why we offer dedicated weekend batches as well as fast-track weekday options. The curriculum, virtual lab access, and quality of training remain exactly the same across all batch types, ensuring you can upskill and transition into a cybersecurity career without disrupting your current job responsibilities.
Q11: Is a free demo class available before enrolling in the Chennai ethical hacking batch?
A: Absolutely, we offer a free demo class where you can experience our teaching methodology, interact with our expert trainers, and get a clear glimpse of the curriculum structure and virtual lab environment. This session is designed to help you evaluate the quality of our training and ensure it aligns perfectly with your learning goals and career expectations before you make any enrollment commitment.
Q12: What is the typical duration of the ethical hacking course?
A: The standard duration of our ethical hacking course is approximately three to four months, covering around 60 to 80 hours of intensive, structured live training and hands-on lab practice. This timeline is carefully designed to give you ample time to grasp complex security concepts, practice extensively on the virtual servers, and complete substantial real-time projects without feeling rushed.
Q13: Will I receive a certification upon completing the ethical hacking training?
A: Yes, upon successful completion of the course and the final capstone project, you will receive an industry-recognized training certificate from Edubrights. While this certificate validates your comprehensive training, we place equal emphasis on helping you build a strong portfolio of security assessments and real-time projects, which together significantly boost your credibility during job interviews.
Q14: Does the course cover mobile application security testing for Android and iOS?
A: Yes, we include a specialized module on mobile application security, teaching you how to assess the security of both Android and iOS applications. You will learn static and dynamic analysis techniques, how to intercept mobile traffic, and how to identify vulnerabilities like insecure data storage and improper session management, which is increasingly relevant for Chennai’s mobile-first tech companies.
Q15: How does the program help traditional IT staff transition to ethical hacking roles?
A: We have designed a specific transition pathway for IT support and network administrators already working in the tech sector. The curriculum builds upon your existing knowledge of networks and systems, introducing security concepts like vulnerability management, log analysis, and exploit development in a contextualized manner. This allows you to leverage your domain expertise while rapidly acquiring the specialized offensive security skills needed for penetration testing roles.
Q16: Are there case studies based on real-world cyber incidents in India?
A: Yes, our training is heavily grounded in reality, featuring detailed case studies of actual cyber incidents that have impacted Indian organizations. We analyze the attack vectors used, the vulnerabilities exploited, and the subsequent remediation steps taken by the affected organizations. This practical, retrospective learning approach ensures you understand the real-world consequences of security lapses and how to prevent similar breaches.
Q17: Does the training include data privacy and legal aspects of hacking in India?
A: Yes, ethics and legality are foundational to our program, and we dedicate specific sessions to the legal frameworks governing cybersecurity in India, such as the Information Technology Act 2000. We emphasize the importance of obtaining proper written authorization before testing any system and instill a strong code of ethics, ensuring you understand the severe legal consequences of unauthorized access and the principles of responsible disclosure.
Q18: What specific job roles can I target after completing this course in Chennai?
A: Upon successful completion, you will be well-prepared to apply for roles such as Ethical Hacker, Penetration Tester, Vulnerability Assessment Specialist, SOC Analyst, and Information Security Consultant. The blend of offensive and defensive knowledge, hands-on project experience, and certification preparation equips you to meet the diverse requirements of these high-demand positions in Chennai’s thriving IT sector.
Q19: Do you teach wireless network security and Wi-Fi hacking prevention?
A: Yes, we cover wireless network security extensively, teaching you how to identify and exploit vulnerabilities in Wi-Fi protocols like WEP, WPA, and WPA2. You will learn how to use tools like Aircrack-ng to capture handshakes and crack passwords, followed by the necessary defensive configurations to secure wireless networks against such attacks and prevent unauthorized access to corporate systems.
Q20: Will I learn how to write professional penetration testing reports for clients?
A: Yes, reporting is a critical deliverable in any security engagement, and we dedicate specific training to writing professional VAPT reports. You will learn how to document vulnerabilities clearly, calculate risk scores using the Common Vulnerability Scoring System, provide actionable remediation steps, and present technical findings to both technical IT teams and non-technical executive stakeholders.
Q21: Is social engineering and phishing simulation part of the curriculum?
A: Yes, human error remains the weakest link in cybersecurity, which is why we cover social engineering tactics in detail. You will learn how attackers manipulate human psychology through phishing, pretexting, and baiting, and more importantly, you will learn how to design and execute simulated phishing campaigns to train employees and strengthen an organization’s human firewall.
Q22: How are mock interviews conducted to prepare students for cybersecurity job interviews?
A: We conduct rigorous, multi-stage mock interviews that simulate real technical and behavioral rounds conducted by top tech companies. These sessions include scenario-based questions on vulnerability exploitation, log analysis, and incident handling, with our trainers providing detailed, constructive feedback to help you refine your technical communication and problem-solving skills under pressure.
Q23: Are study materials, cheat sheets, and recorded sessions provided for the course?
A: Yes, we provide a rich repository of learning resources, including detailed presentation slides, step-by-step lab guides, command cheat sheets, and recorded sessions of all live classes. All these materials are accessible via our Learning Management System, allowing you to review complex topics and replicate lab exercises at your own pace long after the live sessions have ended.
Q24: Does the course cover cloud security and hacking cloud environments?
A: Yes, as enterprises rapidly migrate to the cloud, we dedicate specific modules to Cloud Security. You will learn how to identify and exploit misconfigurations in AWS and Azure environments, understand Identity and Access Management vulnerabilities, and learn how to secure cloud workloads, ensuring you are prepared for modern cloud penetration testing roles.
Q25: Will I learn about malware analysis and reverse engineering basics?
A: Yes, we introduce you to the fundamentals of malware analysis and reverse engineering. You will learn how to set up a safe, isolated sandbox environment, analyze suspicious files using static and dynamic analysis tools, and understand basic assembly language to decipher how malware operates, which is a highly specialized and sought-after skill in threat intelligence.
Q26: Are there opportunities for live internships or industry exposure in Chennai?
A: Yes, we actively facilitate internship opportunities for deserving students with our partner organizations in Chennai. These internships provide invaluable real-world experience, allowing you to work alongside seasoned security professionals on live projects, which significantly enhances your resume and increases your chances of securing a full-time role in the city’s competitive market.
Q27: How does the course keep up with the latest zero-day vulnerabilities and hacking techniques?
A: Our curriculum is continuously reviewed and updated by our expert trainers who are actively working on live security projects in the industry. We regularly incorporate new threat intelligence, zero-day vulnerability case studies, and updated mitigation strategies, ensuring that the skills you learn are exactly what top employers are currently seeking to defend against modern attacks.
Q28: Is soft skills and client communication training included in the program?
A: Absolutely, technical expertise must be paired with strong communication skills to succeed as a security consultant. We integrate soft skills training into the curriculum, focusing on requirement gathering, vulnerability presentation, professional report writing, and effective stakeholder management, which are essential for conducting security workshops and managing client expectations professionally.
Q29: Can I connect with past students who have successfully placed in Chennai IT companies?
A: Yes, we can connect you with our active alumni network so you can hear firsthand about their learning experience and career progression. Speaking with former students who have successfully secured cybersecurity roles provides valuable, realistic insights into how the course helped them and what to expect from our training and placement process.
Q30: Does the training cover Active Directory and Windows environment hacking?
A: Yes, Active Directory is the backbone of most corporate networks, and we cover its security extensively. You will learn about common attack vectors such as Kerberoasting, Pass-the-Hash, and lateral movement techniques, as well as the defensive strategies required to harden Windows environments and detect these advanced persistent threats.
Q31: Are there group projects or Capture The Flag competitions included?
A: Yes, we encourage competitive and collaborative learning by organizing regular Capture The Flag challenges and group security projects. These activities simulate real-world attack scenarios where you must work together to find hidden flags, exploit vulnerabilities, and defend systems, building essential teamwork and rapid problem-solving skills highly valued by hiring managers.
Q32: How does the course prepare students for Security Operations Center analyst roles?
A: We provide specialized training tailored for SOC analyst roles, focusing on log management, threat intelligence, and incident triage. You will learn how to monitor security alerts, differentiate between false positives and genuine threats, and execute standard operating procedures to contain and eradicate cyber incidents, making you immediately productive in a SOC environment.
Q33: Is training provided on endpoint security and antivirus evasion techniques?
A: Yes, we cover endpoint security from both offensive and defensive perspectives. You will learn how modern Endpoint Detection and Response solutions work, and conversely, how attackers use techniques like obfuscation, packing, and living-off-the-land binaries to evade traditional antivirus software, giving you a comprehensive understanding of endpoint threats.
Q34: Do you offer customized corporate ethical hacking training for companies in Chennai?
A: Yes, we offer customized corporate training programs tailored to the specific security maturity and requirements of companies in Chennai. If your organization needs to upskill its IT team on penetration testing, secure coding, or security awareness, we can design a bespoke curriculum and schedule flexible batches to meet your corporate security goals efficiently.
Q35: What is the expected salary trajectory for ethical hacking professionals in Chennai?
A: While salaries vary based on individual performance, prior experience, and the hiring company, entry-level ethical hacking professionals in Chennai typically start with competitive packages that grow rapidly with experience and certifications. With the advanced competencies in penetration testing, SOC operations, and cloud security that you gain from our course, you are well-positioned to negotiate strong starting offers and aim for accelerated career growth.
Q36: How can I register and start my learning journey for the ethical hacking batch in Chennai?
A: You can easily register by visiting our website and filling out the inquiry form, or by calling our admissions team directly. Our dedicated counselors will guide you through the enrollment process, explain the available batch schedules, and help you choose the learning mode that best fits your personal and professional schedule, ensuring a smooth start to your cybersecurity career.
Q37: Does the course cover Internet of Things security and smart device vulnerabilities?
A: Yes, as IoT devices become ubiquitous, we include a module on IoT security. You will learn about the unique attack surfaces of smart devices, common vulnerabilities like default credentials and unencrypted communications, and how to perform basic hardware and firmware analysis to secure connected environments.
Q38: Will I learn how to secure APIs and microservices architectures?
A: Yes, API security is a critical modern requirement, and we teach you how to identify and remediate vulnerabilities specific to APIs, such as broken object level authorization and excessive data exposure. You will learn how to test REST and GraphQL APIs using specialized tools and implement security controls like rate limiting to protect microservices architectures.
Q39: Is there guidance provided on building a freelance career in bug bounty hunting?
A: Yes, for students interested in independent security research, we provide guidance on how to start a career in bug bounty hunting. We cover how to select suitable targets on platforms like HackerOne and Bugcrowd, how to write effective vulnerability reports, and the ethical and legal boundaries of responsible disclosure, helping you potentially earn income while you learn.
Q40: Does the training include scripting for automation in ethical hacking?
A: Yes, manual security testing does not scale, which is why we integrate scripting for automation directly into the training. You will learn how to write Python and Bash scripts to interact with systems, automate routine reconnaissance tasks, parse logs, and build custom security tools, significantly reducing operational overhead and enhancing your hacking capabilities.
Q41: How does the course help students build a strong portfolio for ethical hacking roles?
A: We guide you in building a professional portfolio that showcases your practical skills, such as writing detailed walkthroughs of Capture The Flag challenges, documenting your VAPT project findings, and contributing to open-source security tools on GitHub. A well-maintained portfolio serves as tangible proof of your capabilities to potential employers who value practical expertise over theoretical knowledge.
Q42: Is prior programming knowledge required for this ethical hacking course?
A: While prior programming knowledge is helpful, it is not strictly mandatory as we cover the essential scripting languages required for cybersecurity from the ground up. We focus on teaching Python and Bash scripting specifically tailored for security automation and log analysis, ensuring that you can write custom scripts to automate tasks without needing a computer science degree.
Q43: Does the course cover cryptography and how hackers exploit weak encryption?
A: Yes, cryptography is a foundational pillar of our curriculum that we cover extensively. You will learn how encryption algorithms like AES and RSA work, understand public key infrastructure, and analyze how attackers exploit weak cryptographic implementations or poor key management to intercept and decrypt sensitive financial or personal data.
Q44: Will I learn about privilege escalation techniques in Linux and Windows?
A: Yes, privilege escalation is a critical phase of any penetration test, and we cover it in depth for both Linux and Windows environments. You will learn how to identify misconfigurations, exploit kernel vulnerabilities, and abuse scheduled tasks or services to elevate your access from a standard user to a root or system administrator account.
Q45: Are there specific modules on database security and SQL injection prevention?
A: Yes, database security is a major focus, and we provide extensive hands-on training on SQL injection and NoSQL injection attacks. You will learn how to extract sensitive data from vulnerable databases, bypass authentication mechanisms, and, crucially, how to implement parameterized queries and other defensive coding practices to prevent these attacks.
Q46: How does the training address the security of remote work and VPNs?
A: We cover the security implications of remote work, including the vulnerabilities associated with Virtual Private Networks and remote desktop protocols. You will learn how attackers exploit weak VPN configurations or compromised credentials to gain initial access to corporate networks, and how to implement secure remote access solutions like Zero Trust Network Access.
Q47: Can non-IT professionals or commerce graduates successfully transition into ethical hacking?
A: Yes, non-IT professionals and commerce graduates can successfully transition into cybersecurity, especially in roles like Governance, Risk, and Compliance or SOC analysis. Our course provides the necessary technical foundation while leveraging your existing analytical and process-oriented skills, giving you a unique advantage in understanding business risk and regulatory compliance.
Q48: What makes Edubrights the preferred choice for ethical hacking training over other institutes in Chennai?
A: Edubrights stands out due to our comprehensive curriculum covering both offensive and defensive security, experienced industry trainers, and intense focus on real-world, hands-on projects. Our personalized career support, including portfolio building and dedicated placement assistance, ensures you are not just certified but genuinely job-ready. We prioritize practical skill development and mentorship over mass enrollment, making us the preferred choice for serious cybersecurity aspirants in Chennai.
Q49: Is there post-training support for interview preparation or project queries?
A: Yes, our commitment to your success extends well beyond the final day of the course. We provide ongoing post-training support, which includes continued access to our alumni community, guidance on specific job interview preparations, and assistance in understanding real-world security scenarios you might encounter during your initial months as a professional.
Q50: How does the course address the security of remote work and VPNs?
A: We cover the security implications of remote work, including the vulnerabilities associated with Virtual Private Networks and remote desktop protocols. You will learn how attackers exploit weak VPN configurations or compromised credentials to gain initial access to corporate networks, and how to implement secure remote access solutions like Zero Trust Network Access to protect distributed workforces.
Get Training Quote for Free
Testimonials
Hear What Our Students Say
"Transform your life through Education, hear it from our Alumni"

6 LPA
Fathima
Student
Software Engineer
"Transform your life through Education, hear it from our Alumni"
8 LPA
Rahul
Student
Data Scientist
"Transform your life through Education, hear it from our Alumni"
8 LPA
Siddharth
NIELSON IQ
Data Analyst