Course Objectives
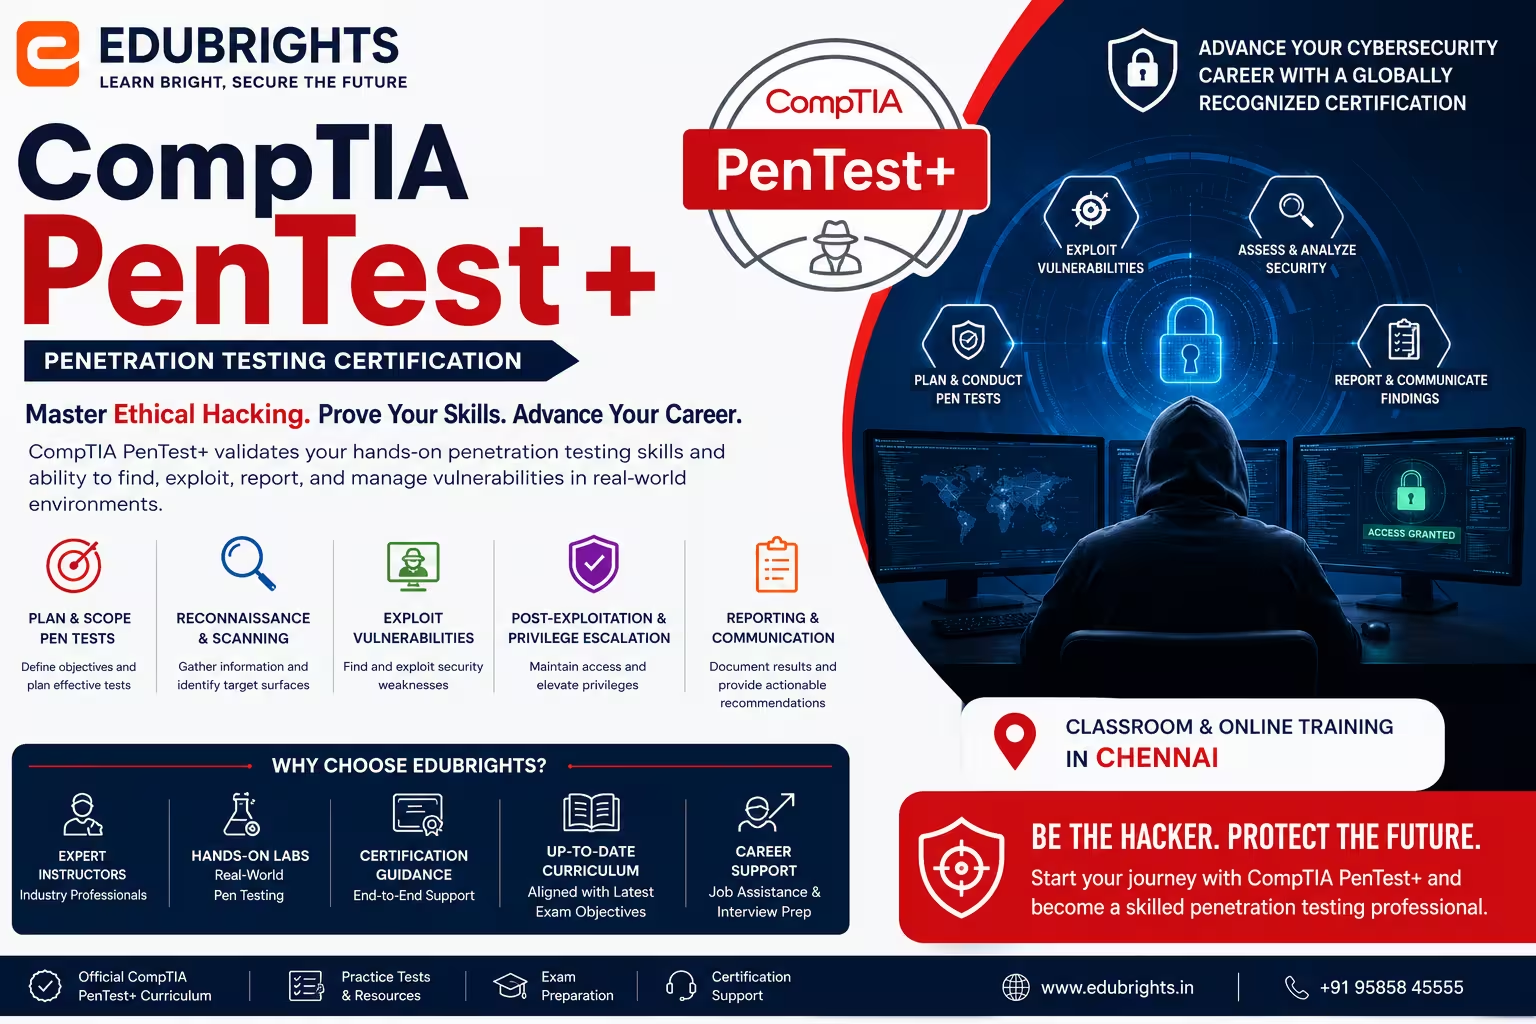
1. Q: What is CompTIA PenTest+?
A: CompTIA PenTest+ is a globally recognized certification that validates penetration testing and vulnerability assessment skills.
2. Q: Why is vulnerability assessment important?
A: It helps identify security weaknesses before attackers can exploit them.
3. Q: What is penetration testing?
A: Penetration testing is the authorized process of identifying and validating security weaknesses in systems.
4. Q: Why is reporting important in penetration testing?
A: It helps organizations understand risks and implement the right security measures.
5. Q: Why should I earn CompTIA PenTest+ certification?
A: It validates practical penetration testing skills and improves cybersecurity career opportunities.
Popular Techniques Covered in This Course
1.Cybersecurity fundamentals
2.Threat detection and mitigation
3.Identity and Access Management (IAM)
4.Risk assessment and management
5.Cryptography and PKI
6.Network security principles
7.Security operations and incident response
8.Endpoint security monitoring
9.Report writing and communication
10.Compliance and legal issues
Get Hands-on Knowledge about Real-Time Projects
Project 1
Project 1: Network Vulnerability Assessment
Description: Identify security weaknesses in a sample enterprise network and recommend remediation steps.
Project 2
Project 2: Web Application Security Assessment
Description: Perform an authorized security assessment of a web application and document the findings.
Project 3
Project 3: Wireless Network Security Review
Description: Evaluate wireless network configurations and identify potential security risks.
Project 4
Project 4: Security Audit and Risk Report
Description: Conduct a security audit and prepare a professional vulnerability assessment report.
Project 5
Project 5: Internal Security Assessment
Description: Assess an organization's internal systems in a controlled environment and recommend security improvements.
Key Features
Edubrights offers CompTIA PenTest+ training in virtual mode with expert trainers. Here are the key features.
40 Hours Course Duration
100% Job Oriented Training
Industry Expert Faculties
Free Demo Class Available
Completed 500+ Batches
Certification Guidance
Curriculum
Module 1: Planning and Scoping
- Governance, risk, and compliance concepts
- Scoping penetration testing engagements
- Ethical and legal considerations
Module 2: Information Gathering and Vulnerability Scanning
- Passive and active reconnaissance techniques
- Use of tools like Nmap and vulnerability scanners
- OSINT and service enumeration
Module 3: Attacks and Exploits
- Network, wireless, and application-based attacks
- Exploiting cloud and specialized systems
- Social engineering and physical attacks
Module 4: Post-Exploitation
- Maintaining access and lateral movement
- Privilege escalation and data extraction
- Detection avoidance techniques
Module 5: Reporting and Communication
- Writing clear technical and business reports
- Delivering remediation recommendations
- Effective stakeholder communication
Module 6: Tools and Code Analysis
- Penetration testing tools overview
- Basic scripting and code review
- Automation and custom tool usage
Receive Training From Our Skilled and Effective Trainers
Experience in the Industry Gain knowledge from experts with practical CompTIA PenTest+ project experience in a variety of sectors.
Backgrounds at the Top Prominent corporations such as HCL, TCS, Accenture, and Cognizant employ trainers.
Clear & Effective Teaching Excellent communication and real-world examples simplify complex subjects.
Hands-On Learning Focus Students can apply their abilities in real-world situations with the use of case studies and real-time projects.
Up-to-Date Knowledge Trainers stay current with the latest tools, techniques, and best practices.
CompTIA PenTest+ Certification Training
Our certification validates your skills in penetration testing and vulnerability management with real-world scenarios and tool usage. Gain expertise critical for security consultants and ethical hackers. Ideal for advancing your cybersecurity career.
Course FAQs
1. What is CompTIA PenTest+ certification?
CompTIA PenTest+ is a cyber security certification focused on penetration testing and security assessment concepts. It covers areas such as planning and scoping, information gathering, vulnerability scanning, security testing, post-exploitation concepts and security assessment reporting.
2. What is CompTIA PenTest+ training in Chennai?
CompTIA PenTest+ training in Chennai provides structured learning for individuals who want to understand penetration-testing methodologies and prepare for the PenTest+ certification. The training covers important concepts such as planning, reconnaissance, vulnerability assessment, security testing, post-exploitation and reporting.
3. Who can join the CompTIA PenTest+ course?
The CompTIA PenTest+ course can be suitable for cyber security learners, IT professionals, network and system administrators, security analysts and individuals who want to develop penetration-testing knowledge. A basic understanding of networking, operating systems and cyber security concepts can be helpful.
4. Is PenTest+ suitable for beginners?
PenTest+ can be challenging for complete beginners because penetration testing involves networking, operating systems, security concepts and technical assessment methods. Beginners can still work toward PenTest+ by first building a foundation in networking, Linux, operating systems and basic cyber security concepts.
5. What are the prerequisites for CompTIA PenTest+?
A basic understanding of networking, operating systems and cyber security concepts can help learners understand PenTest+ topics more effectively. Familiarity with concepts such as IP addressing, common protocols, Linux or command-line environments and security fundamentals can provide a useful foundation.
6. Do I need previous penetration-testing experience?
Previous professional penetration-testing experience is not always necessary for starting a PenTest+ training program. However, learners should have or develop a good understanding of networking, systems and basic cyber security concepts because these fundamentals support penetration-testing and security-assessment learning.
7. Do I need programming knowledge for PenTest+?
Advanced programming knowledge is not necessarily required to begin learning PenTest+ concepts. However, basic scripting and the ability to understand simple code can be useful for tasks such as automation, analyzing scripts and understanding how applications and systems behave during security assessments.
8. What topics are covered in the PenTest+ syllabus?
The CompTIA PenTest+ syllabus covers major penetration-testing concepts such as planning and scoping, information gathering, vulnerability scanning, network and application security testing, post-exploitation concepts, reporting and communication. The exact topics should align with the current PenTest+ exam objectives.
9. Does the course cover planning and scoping?
Yes. Planning and scoping are important parts of penetration testing. Learners can understand how a security assessment is defined, how objectives and boundaries are established and why authorization, scope and rules of engagement are important before conducting authorized security testing.
10. Will I learn information-gathering techniques?
Yes. Information gathering is an important stage of penetration testing. Learners can study how security professionals collect and analyze relevant information about authorized target environments to understand potential attack surfaces and identify areas that may require further assessment.
11. Does the course include vulnerability scanning?
Yes. Vulnerability scanning is an important part of security assessment. Learners can understand how vulnerabilities are identified, analyzed and prioritized, as well as the role of vulnerability scanners and the importance of validating results within an authorized testing environment.
12. Will I learn network and application attacks?
The course can introduce network and application security-testing concepts within authorized and controlled environments. Learners study common attack methods, vulnerabilities and testing approaches to better understand how weaknesses may be identified and how organizations can improve their security controls.
13. Does the course cover wireless security testing?
Wireless security testing concepts may be included as part of understanding how wireless networks can be assessed for potential security weaknesses. Learners can study wireless security principles, common risks and authorized assessment approaches used to evaluate wireless network security.
14. Does the course include cloud and specialised-system security?
The course can introduce security considerations for cloud environments and specialised systems as part of modern penetration-testing and security-assessment concepts. Learners can understand how different technologies may require specific security considerations and assessment approaches.
15. Will I learn post-exploitation concepts?
Yes. Post-exploitation concepts can help learners understand what security professionals may assess after demonstrating an authorized security weakness. The focus is on understanding potential impact, evaluating security controls and documenting findings so organizations can improve their security posture.
16. Does the course cover privilege escalation?
Privilege-escalation concepts can be introduced to help learners understand how weaknesses in systems or configurations may allow unauthorized access levels to increase during an authorized security assessment. Understanding these concepts helps security professionals identify and recommend fixes for potential security weaknesses.
17. Will I learn penetration-testing report writing?
Yes. Reporting is an important part of penetration testing because security findings need to be communicated clearly to technical teams and decision-makers. Learners can understand how assessment findings, risk levels, potential impact and remediation recommendations are documented in a structured security report.
18. Does the course include practical projects?
Practical projects can help learners apply penetration-testing and security-assessment concepts in controlled environments. Depending on the training approach, projects may involve reconnaissance, vulnerability assessment, security testing, analysis of findings and preparation of assessment reports.
19. What jobs can I pursue after PenTest+ certification?
After developing the required technical knowledge and practical skills, learners can explore cyber security roles such as Junior Penetration Tester, Vulnerability Assessment Analyst, Security Analyst, Application Security Associate and Junior Security Consultant. Career opportunities depend on practical skills, professional experience, certifications and employer requirements.
20. What are the CompTIA PenTest+ batch timings in Chennai?
CompTIA PenTest+ batch timings in Chennai can vary depending on the current training schedule and available batches. For the latest information about batch timings, course duration, training mode and upcoming schedules, learners should confirm the current details directly with Edubrights.
Get Training Quote for Free
Testimonials
Hear What Our Students Say
"Transform your life through Education, hear it from our Alumni"

6 LPA
Fathima
Student
Software Engineer
"Transform your life through Education, hear it from our Alumni"
8 LPA
Rahul
Student
Data Scientist
"Transform your life through Education, hear it from our Alumni"
8 LPA
Siddharth
NIELSON IQ
Data Analyst